Best HWID Spoofer Guide for Banned Players
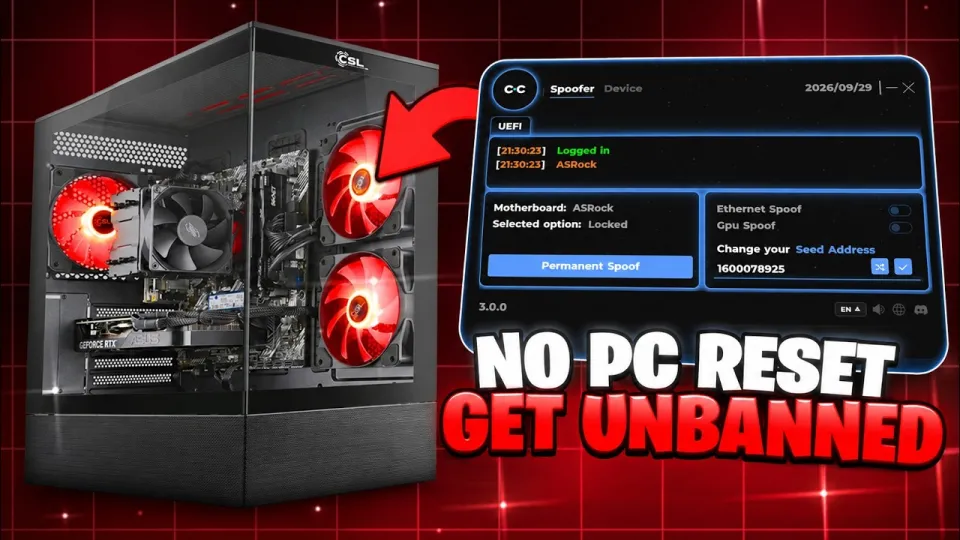
Video: The Ultimate HWID Spoofer Tutorial 2026 – Full Guide To Get Unbanned Fast
Key takeaways
- An HWID spoofer replaces the hardware identifiers anti-cheat systems use to recognise a banned machine, rather than changing the game account itself.
- The spoofer shown in the clixx breakdown is distributed through cethcheats.cc with a Discord community and a 5% discount coupon code DENYS.
- Supported titles listed for the tool include Fortnite, Warzone, Rust, CS2, Rainbow Six Siege, Apex Legends and Valorant.
- The tutorial covers interface overview, feature list, configuration and settings, and the installation process.
- Two spoofing modes dominate the market: temporary (session-based) and permanent (survives reboots until manually reverted).
The best HWID spoofer is a tool that changes the hardware identifiers a game's anti-cheat reads — disk serials, motherboard and SMBIOS data, MAC addresses, volume IDs and similar fingerprints — so a machine flagged by a hardware ban looks like a different PC. The version walked through in the clixx tutorial is distributed through the CethCheats store, which also hosts the vendor's product catalogue and licensing. A spoofer does not restore a banned game account; it only aims to make the computer itself unrecognisable to the anti-cheat.
What an HWID spoofer actually changes
Hardware ID bans work because anti-cheat clients build a fingerprint from several components at once. A typical spoofing suite targets the following:
- Disk and volume serial numbers, including the identifiers Windows exposes per drive.
- SMBIOS and motherboard data — BIOS vendor strings, system UUID, baseboard serial.
- Network adapter MAC addresses, both physical and the ones stored in the registry.
- Windows installation identifiers, machine GUID and product ID entries.
- Registry traces and leftover files that anti-cheat drivers may query on launch.
A permanent spoofer writes these changes so they survive a reboot, while a temporary spoofer applies them only for the current session and reverts on restart. Permanent spoofing is the more common request for games with aggressive hardware bans, but it also carries more risk: if the tool fails mid-write, the machine can end up with inconsistent serials that some games refuse to launch on.
Inside the clixx tutorial: features and settings
The clixx breakdown is structured as a software walkthrough rather than a gameplay montage, and it covers the parts a buyer usually wants to see before paying. The video opens with an overview of the spoofer's interface, then moves through the available features, the configuration and settings panel, and finally the installation process. What that means in practice for anyone following along:
- The interface exposes individual toggles for each hardware group, so you can spoof disks without touching the network adapter, or run a full clean.
- Configuration options let you pick between temporary and permanent behaviour where the build supports both.
- The settings screen is where serial values and profile choices are set before the spoof is applied.
- Installation is handled by the tool itself, which is the step most likely to break if antivirus software interferes.
Because the video has no spoken transcript available, the exact menu labels are best confirmed on the vendor's Discord, where the community posts current build notes. The description lists the store link and an invite to discord.gg/ceth, plus coupon code DENYS for 5% off.
Supported games and compatibility
Compatibility is the question that decides whether a spoofer is worth installing. The tool in the tutorial advertises support for Fortnite, Warzone, Rust, CS2, Rainbow Six Siege, Apex Legends and Valorant, which covers most of the titles where hardware bans are routinely issued. Each of those games uses a different anti-cheat stack — Easy Anti-Cheat in Fortnite and Apex Legends, Vanguard in Valorant, BattlEye in Rainbow Six Siege — and each reads a slightly different set of identifiers, which is why spoofers ship per-game profiles instead of one universal switch.
Practical notes on compatibility:
- Valorant's Vanguard runs at boot and is the least forgiving; a spoof that works for Fortnite may still be detected there.
- Rust and Fortnite bans are frequently hardware-level, which is why those two dominate search interest for spoofers.
- FiveM servers often run their own bans, and a spoofer aimed at GTA/FiveM handles a different identifier set than a competitive shooter build.
- A spoofer update is usually required after a major anti-cheat patch; an outdated build is the most common cause of a failed unban attempt.
Step-by-step setup and safety checks
Setup order matters more than any single setting. A workable sequence, matching the flow shown in the tutorial:
- Disable real-time antivirus protection temporarily and add an exclusion folder — spoofers modify protected registry and disk data, so scanners flag them.
- Create a Windows restore point before the first run, so a failed spoof can be rolled back.
- Launch the spoofer as administrator; without elevated rights the SMBIOS and disk writes silently fail.
- Select the profile for your game, review the hardware groups being changed, and apply the spoof.
- Reboot, then verify the new serials with a system information tool before launching the game.
- Re-enable antivirus and keep the restore point until you have confirmed the game runs.
Two caveats belong in any honest guide. First, spoofing is explicitly against the terms of service of every game listed, and detection can lead to a fresh ban plus the loss of the new hardware fingerprint. Second, paying for a spoofer does not guarantee an unban — anti-cheat vendors update detection continuously, and a build that works today can be flagged within weeks.
How to judge whether a spoofer is the best one
Price is the weakest signal in this market. The stronger indicators are update frequency, transparency about which identifiers are changed, and whether the vendor publishes patch notes after anti-cheat updates. A permanent spoofer that has not been updated since the last Vanguard or EAC patch is worse than useless, because it creates a false sense of safety. Reputable sellers also separate the spoofer licence from any cheat product, since a spoofer alone does not give an advantage in-game and is often bought by players who intend to start clean on a new account.
Before buying, check three things: whether the build supports the specific game and anti-cheat you play, whether the licence is time-limited or lifetime, and whether support happens through a public Discord where you can read other users' reports. The clixx video follows that pattern by showing the interface and settings rather than only the result, which lets a viewer judge the tool's scope before spending money.
Links from the video
- Store and product page: https://cethcheats.cc/
- Community and support: https://discord.gg/ceth
- Discount: coupon code DENYS for 5% off
Conclusion
An HWID spoofer is a hardware-identity tool, not a ban eraser: it changes the serials and identifiers an anti-cheat reads, and the clixx tutorial walks through the interface, feature set, settings and installation of one such build for games including Fortnite, Valorant, Rust and CS2. Treat the setup steps seriously — restore point, administrator rights, reboot and verification — and assume that any spoof can be detected after the next anti-cheat patch. If you want to look at the exact product shown, the CethCheats store is the place to start, and the clixx channel is where the full video breakdown lives.
Source: The Ultimate HWID Spoofer Tutorial 2026 – Full Guide To Get Unbanned Fast · Markdown version
Questions & answers
Does an HWID spoofer actually get your account unbanned?
No. A spoofer changes the hardware identifiers on your PC so the machine is not recognised as previously banned. The banned account itself stays banned; the tool is used to play on a new account from the same computer.
What is the difference between a temporary and a permanent HWID spoofer?
A temporary spoofer applies new identifiers for the current session only and reverts them after a reboot. A permanent spoofer writes the changes so they persist across restarts until you manually restore the originals, which is why a Windows restore point is recommended first.
Which games does the spoofer in the tutorial support?
The listed titles are Fortnite, Warzone, Rust, CS2, Rainbow Six Siege, Apex Legends and Valorant. Because each uses a different anti-cheat — EAC, BattlEye or Vanguard — you need the profile that matches your game and a build updated after the latest anti-cheat patch.
Is using an HWID spoofer safe or allowed?
It is not allowed: spoofing violates the terms of service of every game listed, and detected spoofing can result in another ban. On the technical side, the tool modifies protected system data, so create a restore point, run it as administrator and keep antivirus exclusions temporary.